

This section provides explanations of terminology for beginners. Feel free to add more—the author is just an ordinary person and can't be omniscient
——————————————————————–
TEES TEESimulator or TEESimulator-RS
TS Tricky store
PIF Play Integrity Fix(Inject)
LSPosed is used in Hook software for modification
ZygiskNext provides Zygote support for other modules that require Hook software
 All of the above are modules
KSU KernelSU, a root manager whose branches include SukisuUltra.Sukisu.ReSukisu, and the activation methods for these managers are in mineTutorialApplicable (I think the vast majority of people should know this)
BL Bootloader
ABL is a system partition, standing for Android Bootloader
LKM KernelSU and its branches operate in one of their modes
GKI is the same as above, also known as Built-in
SUSFS GKI mode is hiddenTools(Effect greater than ordinary modules)
Core version Mobile phonesThe factory Android kernel version format:
6.6.89-android15-8-o-g1affdea2379b18
So (everyone should be different)
SELinux acts as a mobile file firewall that blocks illegal commands
Seccomp is a secure computing kernel and a security feature of the Linux kernel
System fingerprint is a piece of data unique to you calculated from your phone
Superuser: Software with root privileges
Module youInstallation/The Magisk/KernelSU module you want to install
KPM is different from modules; KPM provides kernel module installation support
Default Uninstall Module: This is a built-in hidden module provided by KSU, which must be enabled for all software in the detection environment
App Profile system definitionApplicationUID.Data directory.SELinux context.Seccomp rules also serve as the scope lists used by applications like HMA-OSS.LSposed.KSU
Shell/Root are the names of permissions. Shell represents the maximum permissions adb/Shizuku can obtain, while Root is the maximum software permission on the phone (including hardware, such as TEE and SOTERKEY, which are not accessible on the software side).
UID Mobile is a unique ID number assigned by the software (system software 0~9999, regular software 10000+, used for managing data directories)
Package name: The unique name of the software. No two apps with the same package name (in the same user space) cannot appear on your phone.
Post-FS-Data starts the service when the kernel starts up, and the service starts when the system starts
Kernel Build Time The time the kernel is fully written down The format is
#1 SMP PREEMPT Fri May 01 12:00:00 UTC 2026
Please check the exact meaning of each part yourself; I can't explain it clearly anytime soon (if you want to use it, you can copy my section).
SUS (Loop) Path: This is already explained in detail in the SUSFS interface or introduction, so I won't go into it further
Congratulations, you've learned the most common terminology in Root. Next, you'll learn how to get Root/What to do and what not to do after Root
1. Preliminary preparation
1.1 List of Software Tools
Mobile tools:
Aiwan Machine Toolbox
MT Manager
Root manager
HMA-OSS (Hide My Applist)
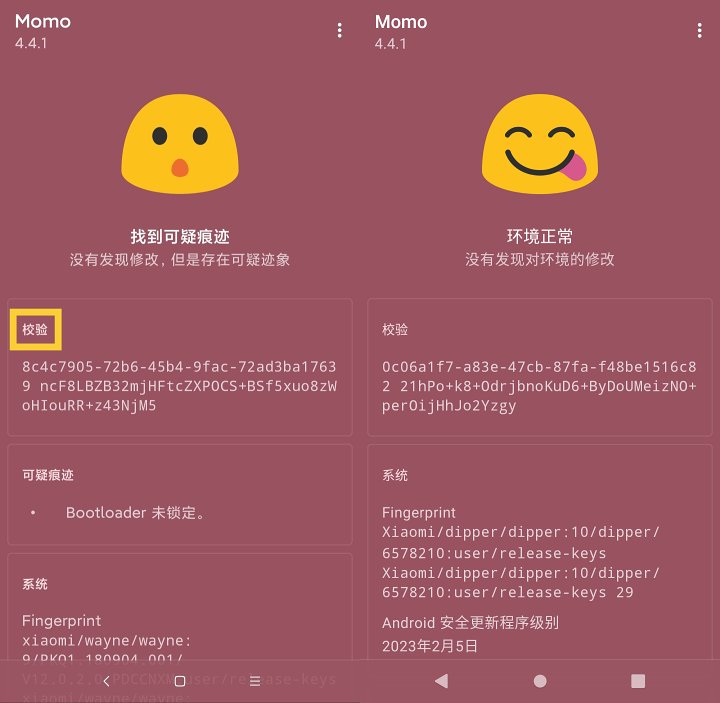
Duckdetector (version 410 or similar, used for environmental detection)
TEESimulator-RS (used to simulate TEE environments, commonly used in Snapdragon devices)
LSPosed
Zygisk Next
Available keybox.xml files (for TEE simulation)
ComputerEnd Tools:
Gadget Assistant (integrates drivers, command line, and other practical functions)
Key Documents:
The official init_boot.img file for the model (Important: Must fully match the current system version; minor version differences may cause issues)
1.2 Initial Phone Setup
1. Request for deep testing (only for devices running ColorOS 16 out of the box): Open the deep test application link in your browser (see resource area at the end of the article), log in to your OPPO account, apply, and wait for approval
2. Enable Developer Options: Go to Settings > About Phone > Version Info, keep tapping the version number until prompted "You are in Developer Mode"
3. Enable the required switch: Go back to Settings > System Settings > Developer Options, and enable OEM Unlock and USB Debugging
1.3 Key DocumentsDownload
Anykernel3 file: GKI is required, LKM is not required
init_boot.img: Files that need to be searched for the corresponding device model and system version from the network; different versions are not interchangeable
keybox.xml: Used for TEESimulator to simulate TEE environments; you need to find it yourself or request it from the author
—
2. Root permission acquisition
2.1 LKM Mode (Relatively Stable, Slightly Weaker Hidden Effect)
Step 1: Generate the patch file
1. Download and open SukisuUltra, then click the gray button on the interface (select file).
2. Use MT Manager to find and select the downloaded init_boot.img
3. Wait for the patch to complete; the log will prompt that output file is written to [file path]
4. This file is usually located at /storage/emulated/0/Download/, with a name similar to kernelsu_patched_****.img. Please copy this file to your computer
Step 2: Unlock the Bootloader (BL)
1. Connect your phone to the computer, enable USB debugging, and use the official data cable
2. When a "Allow USB debugging" popup pops up on your phone, check "Allow all" and confirm
3. Open the phone's "Deep Test" app, tap "Start Application" or "Check Review Status," and follow the prompts to restart your phone to Fastboot mode
4. Open the PC Assistant on your computer and install the Android driver in the Extensions section
5. Open the cmd command line in Gaoji Assistant, confirm the device is connected (shows fastboot device), and enter the command:
“`
fastboot flashing unlock
“`
6. The phone screen will prompt you to confirm unlocking. Press the volume button, select "Unlock," and press the power button to confirm. This operation will format the data partition, and your phone will automatically restart into Recovery mode. Please select "Format Data Partition" to enter the system normally
Step 3: Flash the repair file
1. Put your phone into Fastboot mode again (through in-depth app testing or manually)
2. In the computer's Cmd command line, after confirming the device is connected, enter the following command to flash the repaired init_boot:
“`
fastboot flash init_boot [Full path to the patch file on your computer]
“`
(Tip: You can drag the file directly into the command line window to automatically fill in the path)
3. Seeing Success.Finished. Messages like Total time: X.XXXs indicate success. Press the power button to restart the phone
At this point, you have successfully obtained root access for LKM mode. If you don't want to keep messing around, you can skip the GKI section and go straight to the "Environment Hidden" section
2.2 GKI Mode (Stronger Hidden Effect, Slightly More Complex Process)
Step 1: Obtain the Anykernel3 file
· Recommended channels: Follow and contact developers@Numbersf。
· Build yourself: Visit the designated code repository (see the tutorial below) and follow the tutorial to build it yourself
· Brief build process: Fork repository → Go to Actions → Select Built All OnePlus Kernels → Click Run workflow configuration and run → Download the Anykernel3 file from the successfully built Artifacts
· If stuck at the initialization step, it can be reported to the original author
· The downloaded Anykernel3 file is flashed locally on your phone, rather than using computer fastboot
Step 2: Flash the kernel
1. Store the downloaded Anykernel3.zip files in your phone's storage
2. Open SukisuUltra, click the Working button, select the Anykernel3 kernel, and select the zip file you downloaded
3. Follow the prompts to select other options (usually the default is fine), then click the restart button at the bottom right to complete the flash
—
3. Environment Hidden (Outsmarting Detection Software)
This is the most critical step after rooting, aiming to enable the bank app andGamesand other abnormal environments that are not detected. Core principle: minimize permissions, do not grant root unless necessary; Hide wherever possible, leaving no trace
3.1 General Operation (Applicable to LKM and GKI)
1. Use HMA (Hide My Applist)
Add all your Root-related applications (such as SukisuUltra, MT Manager, LSPosed, etc.) to your blacklist
Enable this blacklist template for the apps you want to hide (such as banking apps, games).
2. Address specific issues identified by the detector
For MT Manager: Open MT Manager, go to Settings, find 'Change MT2 Path', change it to a non-existent path (such as /sdcard/MT2_Hide/), and delete the original MT2 folder
For Zygisk detection: In Zygisk Next settings, enable "Restore mount only", "Use anonymous memory", and "Use Zygisk linker".
3. Zygisk Next configuration
Enable only restore mounting
Anonymous memory is used
Use the Zygisk linker
3.2 GKI mode exclusive enhanced stealth
1. Add a path to the Tricky Store whitelist
In the /data/adb/tricky_store/target.txt file, add the following path:
“`
/system_ext/app/SoterService
/system_ext/app/SoterService/SoterService.apk
“`
This can resolve some detection software "TEE not trusted" errors but may cause the device to be marked as "abnormal"
Snapdragon devices must add it, Dimensity devices can skip it (this step is self-comfort, just fixing errors, games are more likely to get black)
Other options include TWRP backup paths (/storage/emulated/0/TWRP/), etc., added as needed
2. Use SuSFS for application hiding
In the MIUIX interface of SukisuUltra, you can directly select the Root app you want to hide from the "Apps" list
After opening, select the apps at the bottom of the second panel, then select and confirm
3. Simulated TEE environment (Snapdragon devices)
Install TEESimulator-RS and use it together with a valid keybox.xml file
Enable simulation for all applications that need to be tested
TEESimulator will not result in game account bans
4. Replace the LSPosed version
If detection software (such as Chunqiu) reports Miscellaneous Checkout(12) (Zygisk leak), try switching to the latest version of LSPosed-It (which is highly likely not to resolve the issue).
3.3 LKM mode exclusive enhanced camouflage
1. Install additional modules
Install FuseHide and refer to its official documentation for configuration (the author also does not use it often, so requires independent research)
2. Use simulation and hiding
Snapdragon devices can use TEESimulator + keybox.xml.
Used together with HMA and FuseHide
3. Refer to the fourth hidden point exclusive to GKI
—
4. Risk Warnings and Precautions
4.1 Module Versatility
· Software like SukisuUltra and TWRP are mostly customized versions and are not interchangeable across different models
· Some Anykernel3 files are universal, but you need to test them yourself
4.2 Risk of app crashes/account suspension
1. Try to disable all native system debugging options (USB debugging, developer options)
2. Use TEESimulator and keybox.xml to pass key detection points
3. Apply for risk environment use through official channels (approval is basically impossible)
4. For some strong verification apps (such as certain banking apps with Tencent-based software that have strong validation), there may be no solution
4.3 Set security warnings in the system
1. OEM Unlock: After unlocking BL, do not change this option in the settings, as this may cause bricking
2. USB debugging: Some apps detect that turning on makes them unusable; it is recommended to close them when not needed
3. Device Manager: If you don't understand it, do not use it. Do not grant this permission to the virus
4. Accessibility: If possible, don't provide it; it's best to let the virtual machine test it
5. Temperature control files: Non-extreme players are not recommended to modify them; the official tuning is already well balanced
6. Root permission: Please decide whether you need this option
4.4 Data Backup and Brick Removal
· Data backup is the gold standard: before any steps that might modify partitions or unlock data, use TWRP or other tools to fully back up your data
Be sure to disable the lock screen password before operation to prevent TWRP from failing to decrypt the data partition
· Brick Rescue Basics:
· Boot animation freezes: Force restart to enter Recovery or Fastboot
· Infinite restart: Try to disable modules at startup using the computer's ADB command (usually KernelSU will disable it for you, but it's just a backup).
· Black brick: Requires entering Qualcomm 9008 mode (EDL) or sending in for repair (9008 is hardware-level protection; don't say the frame file blocks this interface—it's impossible. In 9008 mode, the computer communicates directly with the chip and doesn't rely on any stored drivers or interface data. The so-called 'unable to connect/send data packets' is actually your phone's circuit break; official authorization is needed to decrypt the packets.)
—
5. Resource acquisition and advancement suggestions
5.1 Oujia Anykernel3 File Resources
· Focus on developers first@Numbersf
· If you need to build it yourself, please visit the designated code repositoryView the link
· Build tutorial (computer required):
1. Register a Github account and remember your password; you need a QQ email or other email address
2. Click the Fork button among the three buttons in the middle right of the screen, then tap the underlined option at the bottom of the navigation interface
3. Tap the Action button in the middle of the screen on the same horizontal line as the Fork key, then select Built All OnePlus Kernels on the left side of the screen
4. Click the Run workflow on the right side of the screen and follow the prompts to configure the settings
5. If you get stuck in the initialization repository and receive an error (red cross) after waiting, report it in the author's comment section. Usually, it will be fixed within a week
6. To download, return to the Action main interface, click Built All OnePlus Kernels, tap the newly built project title in the middle of the screen, scroll down, and at the bottom you'll find the Download option
5.2 Keybox.xml Files
This is a rare resource. Please find it yourself or request it via private message from the author (no guarantee of supply).
Below is a configuration guide for TEESimulator-RS
The author uses the original version without a UI interface, but what I'm sharing with you is a Chinese version with a UI interface. Therefore, I cannot provide you with illustrated tutorials; I will explain in plain text
Click the one under the module
< > opened
Enter the UI interface, click the icon in the top right, then click the leftmost button on the top row (Select All), then click "Keys", select Local Button, select the keybox.xml you downloaded, and save
Below is a guide on how to recover bricks
Since you've already unlocked it, please flash the custom Recovery (I use TWRP myself). Then turn on your computer, connect it, and while off, press and hold the power and volume down for about 5 seconds to enter Fastboot (if the phone is stuck on the first screen at startup, press and hold both volume and power buttons for about 10 seconds to force shutdown). In Fastboot mode, use the volume key to select the "Recovery mode" button and press the power button, and you will enter TWRP. Wait 20 seconds at this point, and you'll enter the main interface. If not, it means you haven't turned off the lock screen password, which means your data can't be saved. However, you can still flash your computer. After connecting to your computer, open the PC Assistant, go to the Recovery mode menu on the left, click it, and a TWRP auto-brick rescue app will appear on the right. Follow the instructions inside
This list includes FB mode brick removal, 9008/EDL brick removal, and Recovery mode removal. You can try it yourself; other modes are simpler to operate
Resource area
The original GitHub address requires some methods to access. You can message the author privately to teach me how to access it, but it costs 8M, so please do not share the method I teach you
ZygiskNext GH original address
View the link
A collection of various versions of LSPoses
View the link
TEESimulator-RS GH Original address
View the link
Aiwan Machine Toolbox
View the link
Gadget assistant
View the link
HMA-OSS GH original address
View the link
Original address of Oka Ak3 GH
View the link



No comments yet